Sunday, 1 September 2019

What you missed in cybersecurity this week

There’s not a week that goes by where cybersecurity doesn’t dominates the headlines. This week was no different. Struggling to keep up? We’ve collected some of the biggest cybersecurity stories from the week to keep you in the know and up to speed.

Malicious websites were used to secretly hack into iPhones for years, says Google

TechCrunch: This was the biggest iPhone security story of the year. Google researchers found a number of websites that were stealthily hacking into thousands of iPhones every week. The operation was carried out by China to target Uyghur Muslims, according to sources, and also targeted Android and Windows users. Google said it was an “indiscriminate” attack through the use of previously undisclosed so-called “zero-day” vulnerabilities.

Hackers could steal a Tesla Model S by cloning its key fob — again

Wired: For the second time in two years, researchers found a serious flaw in the key fobs used to unlock Tesla’s Model S cars. It’s the second time in two years that hackers have successfully cracked the fob’s encryption. Turns out the encryption key was doubled in size from the first time it was cracked. Using twice the resources, the researchers cracked the key again. The good news is that a software update can fix the issue.

Microsoft’s lead EU data watchdog is looking into fresh Windows 10 privacy concerns

TechCrunch: Microsoft could be back in hot water with the Europeans after the Dutch data protection authority asked its Irish counterpart, which oversees the software giant, to investigate Windows 10 for allegedly breaking EU data protection rules. A chief complaint is that Windows 10 collects too much telemetry from its users. Microsoft made some changes after the issue was brought up for the first time in 2017, but the Irish regulator is looking at if these changes go far enough — and if users are adequately informed. Microsoft could be fined up to 4% of its global annual revenue if found to have flouted the law. Based off 2018’s figures, Microsoft could see fines as high as $4.4 billion.

U.S. cyberattack hurt Iran’s ability to target oil tankers, officials say

The New York Times: A secret cyberattack against Iran in June but only reported this week significantly degraded Tehran’s ability to track and target oil tankers in the region. It’s one of several recent offensive operations against a foreign target by the U.S. government in recent moths. Iran’s military seized a British tanker in July in retaliation over a U.S. operation that downed an Iranian drone. According to a senior official, the strike “diminished Iran’s ability to conduct covert attacks” against tankers, but sparked concern that Iran may be able to quickly get back on its feet by fixing the vulnerability used by the Americans to shut down Iran’s operation in the first place.

Apple is turning Siri audio clip review off by default and bringing it in house

TechCrunch: After Apple was caught paying contractors to review Siri queries without user permission, the technology giant said this week it will turn off human review of Siri audio by default and bringing any opt-in review in-house. That means users actively have to allow Apple staff to “grade” audio snippets made through Siri. Apple began audio grading to improve the Siri voice assistant. Amazon, Facebook, Google, and Microsoft have all been caught out using contractors to review user-generated audio.

Hackers are actively trying to steal passwords from two widely used VPNs

Ars Technica: Hackers are targeting and exploiting vulnerabilities in two popular corporate virtual private network (VPN) services. Fortigate and Pulse Secure let remote employees tunnel into their corporate networks from outside the firewall. But these VPN services contain flaws which, if exploited, could let a skilled attacker tunnel into a corporate network without needing an employee’s username or password. That means they can get access to all of the internal resources on that network — potentially leading to a major data breach. News of the attacks came a month after the vulnerabilities in widely used corporate VPNs were first revealed. Thousands of vulnerable endpoints exist — months after the bugs were fixed.

Grand jury indicts alleged Capital One hacker over cryptojacking claims

TechCrunch: And finally, just when you thought the Capital One breach couldn’t get any worse, it does. A federal grand jury said the accused hacker, Paige Thompson, should be indicted on new charges. The alleged hacker is said to have created a tool to detect cloud instances hosted by Amazon Web Services with misconfigured web firewalls. Using that tool, she is accused of breaking into those cloud instances and installing cryptocurrency mining software. This is known as “cryptojacking,” and relies on using computer resources to mine cryptocurrency.


from TechCrunch https://ift.tt/32i4syG

Police hijack a botnet and remotely kill 850,000 malware infections

In a rare feat, French police have hijacked and neutralized a massive cryptocurrency mining botnet controlling close to a million infected computers.

The notorious Retadup malware infects computers and starts mining cryptocurrency by sapping power from a computer’s processor. Although the malware was used to generate money, the malware operators easily could have run other malicious code, like spyware or ransomware. The malware also has wormable properties, allowing it to spread from computer to computer.

Since its first appearance, the cryptocurrency mining malware has spread across the world, including the U.S., Russia, and Central and South America.

According to a blog post announcing the bust, security firm Avast confirmed the operation was successful.

The security firm got involved after it discovered a design flaw in the malware’s command and control server. That flaw, if properly exploited, would have “allowed us to remove the malware from its victims’ computers” without pushing any code to victims’ computers, the researchers said.

The exploit would have dismantled the operation, but the researchers lacked the legal authority to push ahead. Because most of the malware’s infrastructure was located in France, Avast contacted French police. After receiving the go-ahead from prosecutors in July, the police went ahead with the operation to take control of the server and disinfect affected computers.

The French police called the botnet “one of the largest networks” of hijacked computers in the world.

The operation worked by secretly obtaining a snapshot of the malware’s command and control server with cooperation from its web host. The researchers said they had to work carefully as to not be noticed by the malware operators, fearing the malware operators could retaliate.

“The malware authors were mostly distributing cryptocurrency miners, making for a very good passive income,” the security company said. “But if they realized that we were about to take down Retadup in its entirety, they might’ve pushed ransomware to hundreds of thousands of computers while trying to milk their malware for some last profits.”

With a copy of the malicious command and control server in hand, the researchers built their own replica, which disinfected victim computers instead of causing infections.

“[The police] replaced the malicious [command and control] server with a prepared disinfection server that made connected instances of Retadup self-destruct,” said Avast in a blog post. “In the very first second of its activity, several thousand bots connected to it in order to fetch commands from the server. The disinfection server responded to them and disinfected them, abusing the protocol design flaw.”

In doing so, the company was able to stop the malware from operating and remove the malicious code to over 850,000 infected computers.

Jean-Dominique Nollet, head of the French police’s cyber unit, said the malware operators generated several million euros worth of cryptocurrency.

Remotely shutting down a malware botnet is a rare achievement — but difficult to carry out.

Several years ago the U.S. government revoked Rule 41, which now allows judges to issue search and seizure warrants outside of their jurisdiction. Many saw the move as an effort by the FBI to conduct remote hacking operations without being hindered by the locality of a judge’s jurisdiction. Critics argued it would set a dangerous precedent to hack into countless number of computers on a single warrant from a friendly judge.

Since then the amended rule has been used to dismantle at least one major malware operation, the so-called Joanap botnet, linked to hackers working for the North Korean regime.


from TechCrunch https://ift.tt/2ZqtezE

Week in Review: Apple makes a rare apology, Nintendo tries to reinvent its invention

Hey. This is Week-in-Review, where I give a heavy amount of analysis and/or rambling thoughts on one story while scouring the rest of the hundreds of stories that emerged on TechCrunch this week to surface my favorites for your reading pleasure.

Last week, I talked about Google’s Android naming switch-up.


The big story

Like clockwork, sources have been revealing to publications that Siri, Alexa, Google Assistant and Facebook M aren’t just digital assistants, they are portals into the AI workflows of Silicon Valley. Oh, and “AI workflows” means lots of contractors putting in quite a bit of manual work to understand what we want when we ask them questions.

This week, Apple announced that it’s completely changing how it handles reviewing audio from user Siri requests to ensure that users know exactly what they’re getting into privacy-wise.

The big change is that third-party contractors won’t have access to any of the clips for a process called “grading” and there is an explicit opt-in process for users. The company also gave a pretty explicit apology, which is pretty rare for an entity that seems to think its MacBook keyboards are still completely fine.

This whole situation is important for a couple reasons. One, Apple really sets the tone for consumer privacy among the tech giants so making notable changes here is positive and might push others to make similar updates. Two, Apple has the worst consumer-facing digital assistant. Like, Siri is just unquestionably worse than Alexa and Google Assistant so they arguably have the most to lose here and this is a decision that means less data for the company to hone its tech on.

Together, all of these gaffes really weren’t egregious, they were dealing with data that wasn’t nominally connected to users, but audio files should definitely be treated with a little more respect than anonymous crash reports. The journalism from publications like The Guardian pushing on “common” industry practices seemed to surface some positive change here.

Send me feedback
on Twitter @lucasmtny or email
lucas@techcrunch.com

On to the rest of the week’s news.

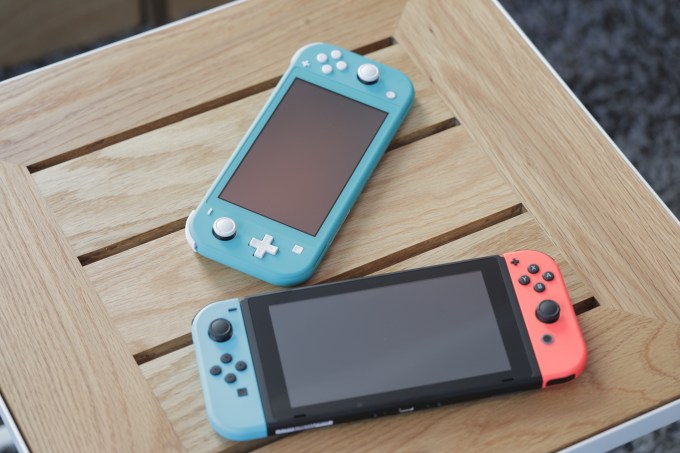
Nintendo Switch Lite

Trends of the week

Here are a few big news items from big companies, with green links to all the sweet, sweet added context:

  • Nintendo’s portable gets more portable
    The Nintendo Switch has been a huge success for the company, but in a new hardware update, the giant is doubling down on portability and simplicity in what might be a bid to capture some of the market it’s left behind from the DS line. Read more about it here.
  • Former Google engineer gets indicted
    Autonomous tech guru Anthony Levandowski who was as the center of the contentious Waymo-Uber lawsuit is back in the spotlight after he was handed a federal indictment with 33 counts of theft and attempted theft of trade secrets. Read more here.
  • Apple’s next hardware event is on its way
    The company just sent out invites to reporters for its iPhone event this month. Read more here.
  • Jack gets hacked
    Twitter like to dream about its impact and influence in ways that feel less realistic to the average user scrolling through spam and insults, but CEO Jack Dorsey got a taste of the seedy underbelly of the site when his Twitter account was hacked Friday and bomb threats and racial slurs were sent out. Read more here.

youtube

GAFA Gaffes

How did the top tech companies screw up this week? This clearly needs its own section, in order of badness:

  1. YouTube’s conspiracy theory devolution:
    [YouTube to reduce conspiracy theory recommendations]
  2. Facebook brings in some long overdue political advertising oversight:
    [Facebook will require political advertisers provide further credentials or have their ads paused]
An Amazon logo seen outside a building in Toronto

Photo by Dinendra Haria/SOPA Images/LightRocket via Getty Images

Extra Crunch

Our premium subscription service had another week of interesting deep dives. We published a roadmap for entrepreneurs looking to leverage Amazon and other ad platforms to create a direct-to-consumer startup.

How to use Amazon and advertising to build your D2C startup

“…This article focuses on customer acquisition, particularly Amazon and online advertising, for the direct-to-consumer (D2C) CPG venture. Selling on Amazon, specifically third-party (3P), has become an increasingly important component of the D2C playbook. About 46% of product searches start on Amazon, which makes it a compelling source of sales even for early-stage ventures….” (Extra Crunch membership required.)

Here are some of our other top reads this week for premium subscribers. This week, we published some analysis on the latest VMware deal and also looked at how startups should integrate customer success solutions early-on.

Sign up for more newsletters in your inbox (including this one) here.


from TechCrunch https://ift.tt/2LesULS

Saturday, 31 August 2019

China used iPhone hacks to target Uyghur Muslims: sources

A number of malicious websites used to hack into iPhones over a two-year period were targeting Uyghur Muslims, TechCrunch has learned.

Sources familiar with the matter said the websites were part of a state-backed attack — likely China — designed to target the Uyghur community in the country’s Xinjiang state.

It’s part of the latest effort by the Chinese government to crack down on the minority Muslim community in recent history. In the past year, Beijing has detained more than a million Uyghurs in internment camps, according to a United Nations human rights committee.

Google security researchers found and recently disclosed the malicious websites this week, but until now it wasn’t known who they were targeting.

The websites were part of a campaign to target the religious group by infecting an iPhone with malicious code simply by visiting a booby-trapped web page. In gaining unfettered access to the iPhone’s software, an attacker could read a victim’s messages, passwords, and track their location in near-real time.

Apple fixed the vulnerabilities in February in iOS 12.1.4, days after Google privately disclosed the flaws. News of the hacking campaign was first disclosed by this week.

These websites had “thousands of visitors” per week for at least two years, Google said.

Victims were tricked into opening a link, which when opened would load one of the malicious websites used to infect the victim. It’s a common tactic to target phone owners with spyware.

One of the sources told TechCrunch the websites used to infect iPhones had been inadvertently indexed by Google’s search engine, prompting the FBI to alert Google to ask for the site to be removed from its index to prevent infections, they added.

A Google spokesperson would not comment beyond the published research. A FBI spokesperson said they could neither confirm nor deny any investigation, and did not comment further.

Google faced some criticism following its bombshell report for not releasing the websites used in the attacks. The researchers said the attacks were “indiscriminate watering hole attacks” with “no target discrimination,” noting that anyone visiting the site would have their iPhone hacked.

But the company would not say who was behind the attacks.

Apple did not comment. An email requesting comment to the Chinese consulate in New York was unreturned.


from TechCrunch https://ift.tt/2ZH5pPx

Tesla’s Model 3 interior (even the steering wheel) is now 100% leather-free

Tesla said Saturday that its Model 3 interiors are now completely free of leather, fulfilling a promise made by CEO Elon Musk at this year’s annual shareholder meeting.

Tesla has been closing in on a leather-free interior for a couple of years now. But a sticking point was the steering wheel, which Musk made mention of at the company’s shareholder meeting in June in response to a request from PETA activist.

“I believe we were close to having a non-heated steering wheel, that’s not leather,” Musk said at the time. “There are some challenges when when heat the non-leather material and also how well it wears over time.”

Musk said Model Y and Model 3 would be vegan by 2020. He wasn’t sure if the company would be able to meet that same goal for the Model S and X.


Activist shareholders made a proposal in 2015 that Tesla no longer use animal-derived leather in the interiors of its electric vehicles by 2019. While stockholders rejected that proposal, Tesla did begin rolling out more “vegan” interior components in its cars.

The company began by offering leather-free seats as an option. Two years ago, Tesla made the synthetic material standard in its Model 3, Model X and Model S vehicles.


from TechCrunch https://ift.tt/2UhMEAQ